Safeguarding: Meeting Funder Expectations for UK Charities and CICs
Safeguarding is more than just a policy document; it's a fundamental commitment to protecting the people your organisation engages with. For UK charities and Community Interest Companies (CICs), a robust safeguarding policy isn't merely good practice, it's often a prerequisite for securing valuable funding. Funders need assurance that you have the systems and culture in place to keep children and vulnerable adults safe from harm, abuse, and neglect.
This comprehensive guide will walk you through exactly what UK funders expect to see in your safeguarding arrangements, helping you not only meet compliance requirements but also build a truly safe environment for everyone involved in your work.
Key takeaways:
- Your safeguarding policy must name a designated lead and clearly define its scope.
- Funders look for clear reporting routes for concerns, whether internal or external.
- Regular trustee review and sign-off are crucial for demonstrating accountability.
- Training, DBS checks, and a strong safeguarding culture are as important as the policy itself.
Understanding the Importance of Safeguarding for Funders
Funders, whether large trusts, foundations, or governmental bodies, are increasingly scrutinising the safeguarding practices of organisations they support. This isn't just about avoiding reputational damage; it's about ethical responsibility and legal compliance. Organisations that receive public or charitable funds are expected to uphold the highest standards of safety and welfare for those they serve. A well-constructed safeguarding policy demonstrates your organisation's commitment and capability in this critical area, building trust and confidence with potential funders.
Without adequate safeguarding, an organisation faces significant risks, including legal challenges, loss of public trust, and, crucially, an inability to secure future funding. Funders want to see that you've thought deeply about potential risks and have concrete measures in place to mitigate them, protecting both the people you support and your organisation's reputation.
What Does a Funder-Ready Safeguarding Policy Look Like?
While the specific format may vary, a strong safeguarding policy for UK funders typically includes several key elements. It's a living document that reflects your organisation's unique activities, the people you work with, and your structure. Here's a breakdown of the essential components:
1. Clear Statement of Intent and Scope
Your policy should begin with a clear, unequivocal statement of your organisation's commitment to safeguarding. This sets the tone and demonstrates your top-level dedication. Equally important is defining the policy's scope: who does it apply to? This typically includes children (under 18) and vulnerable adults, defining what constitutes a 'vulnerable adult' in your specific context (e.g. someone with a learning disability, mental health issue, or physical impairment, who may be unable to protect themselves from harm).
Expert Tip: Don't just copy and paste. Tailor your policy to your specific activities. If you run a youth music project, your risks and procedures will differ from a charity supporting older adults in their homes. Funders can spot generic policies a mile off.
2. Designated Safeguarding Lead (DSL) and Responsibilities
Every funder-ready safeguarding policy must name a specific individual responsible for safeguarding. This person is your Designated Safeguarding Lead (DSL) or equivalent. Their role is pivotal, acting as the first point of contact for concerns, overseeing reporting, and ensuring compliance. The policy should clearly outline their responsibilities, which typically include:
- Receiving and recording safeguarding concerns.
- Liaising with external agencies (e.g. social services, police).
- Providing advice and guidance to staff and volunteers.
- Ensuring appropriate training is delivered.
- Keeping up-to-date with best practice and legislative changes.
It's also good practice to name a deputy DSL, ensuring continuity of cover.
3. Reporting Procedures and Pathways
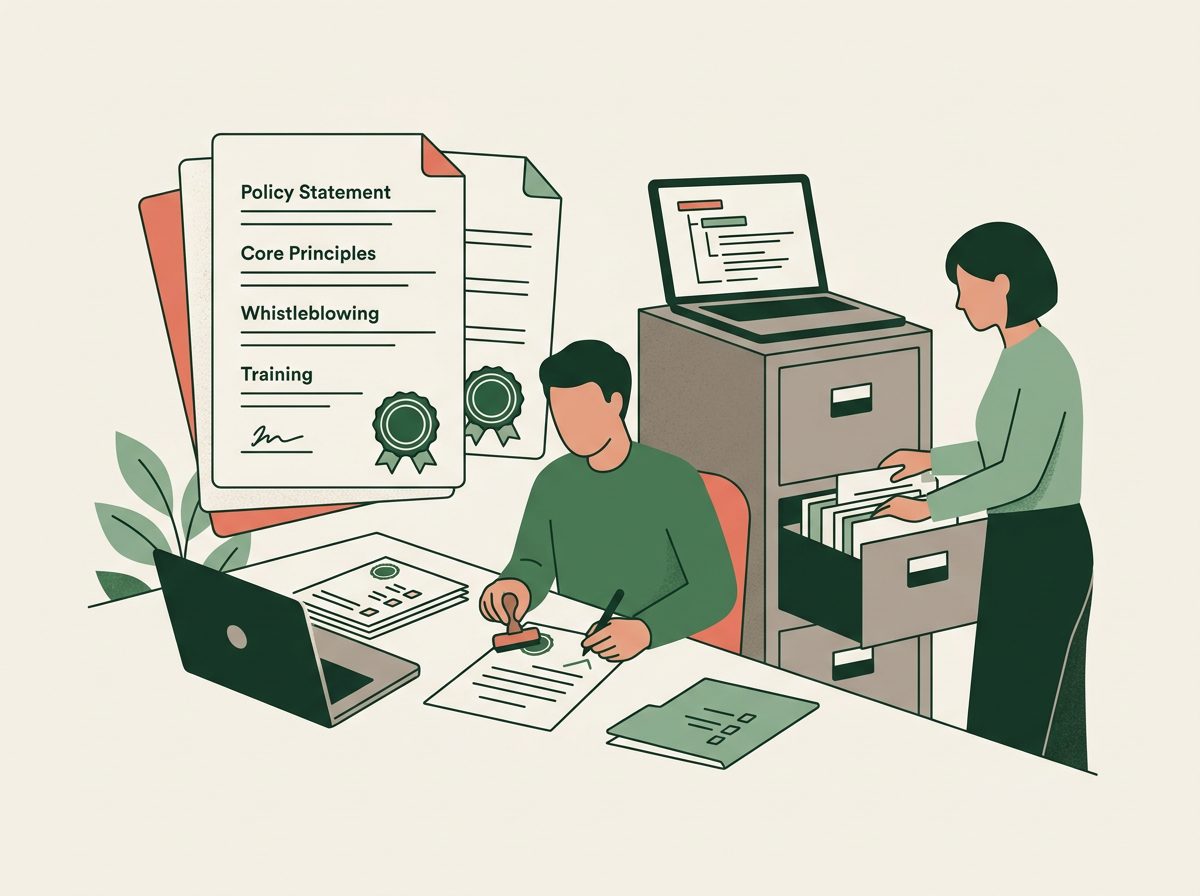
This is arguably the most critical section. Your policy must detail clear, step-by-step procedures for reporting concerns, both internal and external. Staff, volunteers, beneficiaries, and even members of the public need to know how to raise an issue and what will happen next. This should cover:
- Internal reporting: How staff and volunteers report concerns to the DSL.
- External reporting: When and how to report concerns to local authority social care (children's or adult services) or the police. This should include contact details where possible.
- Whistleblowing: A clear separate process for raising concerns about colleagues or senior management, ensuring staff feel safe to speak up without fear of reprisal.
- Confidentiality: Guidance on information sharing and confidentiality, balancing privacy with the need to protect individuals.
4. Recruitment, Training, and DBS Checks
Preventative measures are highly valued by funders. Your policy should outline your commitment to safe recruitment practices, which includes:
- Recruitment: Robust procedures for recruiting staff and volunteers who work with children or vulnerable adults, including application forms, interviews, references, and identity checks.
- DBS Checks: A clear policy on Disclosure and Barring Service (DBS) checks (enhanced DBS for regulated activities is usually required). This should specify who needs a DBS check, how often they are renewed, and how any disclosures are handled.
- Training: A commitment to providing regular, appropriate safeguarding training for all staff and volunteers, tailored to their roles and responsibilities. This should cover recognising signs of abuse, reporting procedures, and how to act safely.
5. Review, Monitoring, and Accountability
A static policy gathering dust in a folder is of little use. Funders want to see that your safeguarding commitment is ongoing. This means:
- Annual Review: A commitment to review the policy at least annually, or sooner if there are significant changes in legislation, guidance, or your organisational activities.
- Trustee Approval: Evidence that the policy has been formally approved and minuted by your board of trustees or directors. This demonstrates high-level oversight and accountability.
- Monitoring: How you monitor the effectiveness of your safeguarding arrangements (e.g. through incident logs, training records, feedback).
Template Outline for Your Safeguarding Policy
You don't need to start from scratch. Use this outline as a framework:
| Section | Key Elements to Include |
|---|---|
| Introduction & Statement of Intent | Organisation's commitment statement, scope (who/what it covers), definitions of child/vulnerable adult, relevant legislation. |
| Roles & Responsibilities | Named DSL/Deputy, their responsibilities, responsibilities of trustees, staff, and volunteers. |
| Recognising & Responding to Concerns | Signs of abuse/neglect, internal reporting steps, external reporting procedures (LA, police), emergency contacts. |
| Safe Practice Procedures | Recruitment (DBS, references), training, code of conduct, digital safeguarding, complaints procedure, anti-bullying. |
| Policy Review & Dissemination | Annual review date, trustee approval, how the policy is communicated to all stakeholders. |
Beyond the Policy: Cultivating a Safeguarding Culture
While a robust policy is essential, funders also look for evidence of a 'safeguarding culture' within your organisation. This means safeguarding isn't just a document; it's embedded in everything you do. Consider these points:
- Openness: Do staff and volunteers feel comfortable raising concerns without fear of reprisal?
- Training: Is training ongoing and relevant, not just a one-off event?
- Communication: Is safeguarding information easily accessible to everyone?
- Leadership: Do senior leaders and trustees actively champion safeguarding?
- Feedback: Do you actively seek feedback from beneficiaries and stakeholders about their safety and experience?
Demonstrating this wider commitment will significantly strengthen your funding applications.
Next steps
Review your current safeguarding policy against the points raised in this article. Ensure your Designated Safeguarding Lead is fully aware of their responsibilities and that all staff and volunteers have received appropriate training. Prioritise an annual review by your trustees, minuting their sign-off, and proactively communicate your safeguarding commitment in all funding applications.